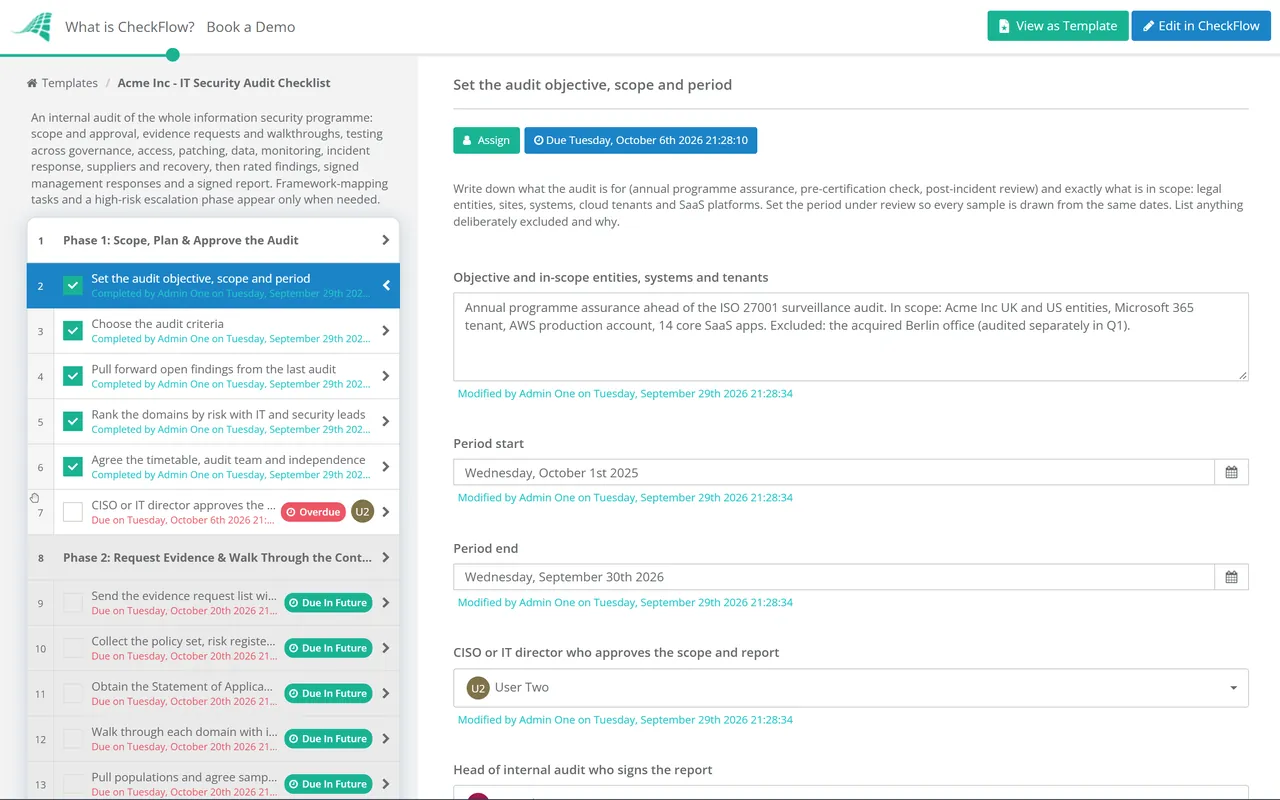
| Governance & policy | Policies approved, owned and reviewed; security reported to leadership | Policy register, approval minutes, board or committee papers | CSF GV.PO, GV.OV · ISO 5.1 · CIS: no single control · SOC 2 CC1, CC5.3 |
| Risk assessment | Assessment current and complete; treatment decisions recorded | Risk register, methodology, treatment plan | CSF ID.RA, GV.RM · ISO clause 6.1.2 · SOC 2 CC3.2 |
| Asset inventory | Hardware, software, cloud and SaaS in use are all recorded | Inventory export, discovery scan, reconciliation sample | CSF ID.AM · ISO 5.9 · CIS 1, 2 · SOC 2 CC6.1 |
| Identity & access | Joiners, movers and leavers handled on time; privileged access and MFA | HR leaver list vs directory, access review sign-offs, admin list | CSF PR.AA · ISO 5.15–5.18, 8.2, 8.5 · CIS 5, 6 · SOC 2 CC6.1–CC6.3 |
| Endpoints, patching & vulnerabilities | Patch timeliness, scan coverage, anti-malware and hardening | Patch compliance report, scan results, exception register | CSF PR.PS, ID.RA · ISO 8.7, 8.8, 8.9 · CIS 4, 7, 10 · SOC 2 CC6.8, CC7.1 |
| Network & cloud (summary) | Boundary controls reviewed; cloud configuration monitored | Firewall review record, cloud posture report | CSF PR.IR · ISO 8.20, 5.23 · CIS 12, 13 · SOC 2 CC6.6 |
| Data protection | Classification applied; encryption at rest and in transit | Classification policy, encryption settings, DLP reports | CSF PR.DS · ISO 5.12, 8.24 · CIS 3 · SOC 2 CC6.7, C1.1 |
| Backup & restore | Backups complete, protected and restorable | Backup job logs, restore test record | CSF PR.DS · ISO 8.13 · CIS 11 · SOC 2 A1.2, A1.3 |
| Logging & monitoring | Coverage of key systems, retention, alert triage | Log source list, SIEM rules, alert tickets | CSF DE.CM, DE.AE · ISO 8.15, 8.16 · CIS 8, 13 · SOC 2 CC7.2 |
| Incident response | Plan current and tested; incidents handled and reported on time | IR plan, exercise report, incident records | CSF RS.MA, RS.CO · ISO 5.24–5.28 · CIS 17 · SOC 2 CC7.3–CC7.5 |
| Third-party security | Suppliers risk-assessed, contracted and reviewed | Supplier register, assessments, SOC reports received | CSF GV.SC · ISO 5.19–5.22 · CIS 15 · SOC 2 CC9.2 |
| Awareness & training | Completion, timeliness for joiners, phishing follow-up | Training records, phishing campaign results | CSF PR.AT · ISO 6.3 · CIS 14 · SOC 2 CC1.4, CC2.2 |
| Business continuity & DR | Plans current, tested, recovery targets met | BIA, DR test report, lessons-learned actions | CSF RC.RP, PR.IR · ISO 5.29, 5.30 · SOC 2 CC9.1, A1.3 |