
Fine for the simple case
Covers: deleting the email and blocking the sender.
Misses: other recipients, clicks, credential use, inbox rules and payment requests.
Record: usually a one-line resolution note.
No Credit Card Required
Printed from checkflow.io/templates/cybersecurity/phishing-incident-response-checklist
A phishing report usually lands with whoever is on the service desk or security queue that day, and what happens next depends on how experienced that person is. One analyst deletes the email and closes the ticket. Another checks who else received it, finds two people who clicked, and discovers a forwarding rule quietly copying the finance director’s mail to an outside address. This free phishing incident response checklist makes the second outcome the normal one. It takes a reported phishing email from triage to closure: analysing the message and scoping who received, clicked, entered credentials, opened attachments or approved MFA prompts, purging it from mailboxes, then branching into credential compromise, business email compromise or malware only when the scoping answers say so. It runs as a sub-playbook of the Cybersecurity Incident Response Checklist and hands over to it when a phish turns out to be the start of something larger.
Most phishing reports are the easy kind: the email arrived, the person who reported it did not click, and the job is to remove it from everyone else’s inbox and block the sender. A general incident response plan is too heavy for that, and a service desk ticket is too light for the cases that are not easy. The difficulty is that you cannot tell which kind you have until you have asked the right questions. Did anyone else click? Did anyone enter a password on the fake sign-in page? Did anyone approve an MFA prompt they did not start? Was a payment or a change of bank details requested, and was it actioned?
Those answers decide everything that follows. A stolen password with a stolen session token is an account takeover, and resetting the password alone does not end it: the attacker may still hold a valid session, may have registered their own MFA method, created an inbox rule to hide replies, or granted a malicious app access to the mailbox. A changed bank detail is a fraud with a deadline measured in hours, because recovery depends on the bank acting before the money moves on. An opened attachment is a possible malware infection on an endpoint. Each of those is a short, specific branch, and this checklist only shows the branches the scoping answers call for.
Covers: deleting the email and blocking the sender.
Misses: other recipients, clicks, credential use, inbox rules and payment requests.
Record: usually a one-line resolution note.
Covers: triage, scoping, purge, and the credential, payment fraud and malware branches when they apply.
Owner: the security analyst, with finance and the identity team pulled in by name.
Record: who received, who clicked and what was done, with times.
Covers: lateral movement, data access, ransomware and regulatory reporting.
Trigger: evidence that the attacker used access beyond one mailbox or device.
Record: the incident timeline, opened from this checklist.
If the scoping shows the attacker read mailboxes holding personal data, the Data Breach Response Checklist takes over the notification decisions. If the payload was ransomware, the Ransomware Response Checklist takes over containment.
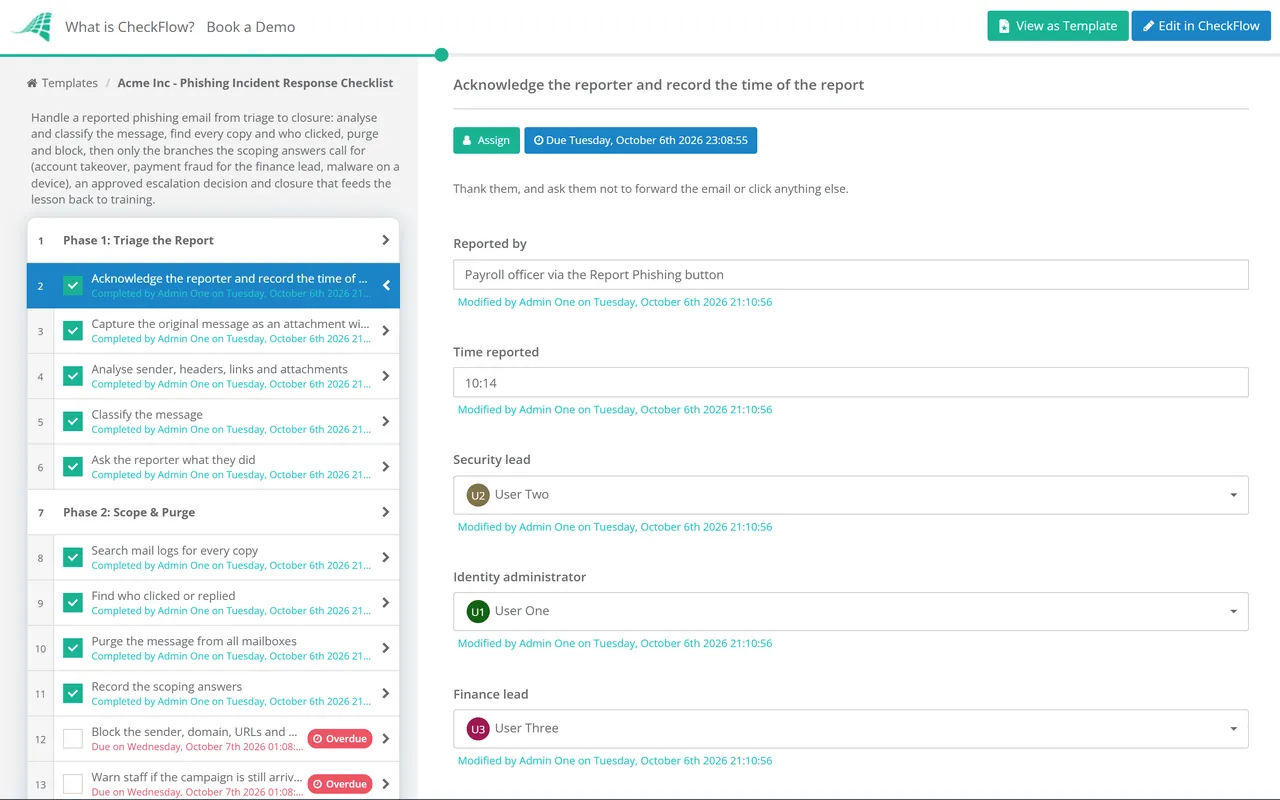
Seven phases take a reported phishing email from triage to closure. Phases 3, 4 and 5 appear only when the scoping answers in Phase 2 call for them.
Owned by the on-duty security or service desk analyst.
Each answer in task 4 is a required Yes/No DropDown. Those answers decide whether Phases 3, 4 and 5 appear.
Appears only when Phase 2 records credentials entered or an MFA prompt approved. Assigned to the identity administrator.
Appears only when Phase 2 records a payment or bank detail change request. Tasks are assigned to the finance lead, not IT.
Appears only when Phase 2 records an attachment opened or a file run. Assigned to the endpoint team.
The escalation decision is an approval step for the security lead.
Closure needs approval from the security lead.
The scoping answers recorded in Phase 2 decide the shape of the response. A clean report moves straight from purge to closure in a few minutes. A report where someone typed a password and a supplier’s bank details changed pulls in the identity administrator and the finance lead, each with their own tasks, without anyone having to remember to call them.
| What Phase 2 records | What appears | First action | Owner |
|---|---|---|---|
| Received only, nobody clicked | Phases 6 and 7 only | Purge, block, give the reporter feedback | Analyst |
| Clicked, no credentials entered | Phases 6 and 7, with the click list attached | Check the site and any download, then purge | Analyst |
| Credentials entered on a fake page | Phase 3: Contain compromised accounts | Reset password and revoke sessions | Identity administrator |
| Unexpected MFA prompt approved | Phase 3: Contain compromised accounts | Revoke sessions, then review registered MFA methods | Identity administrator |
| Payment or bank detail change requested | Phase 4: Business email compromise | Hold the payment and verify on a known number | Finance lead |
| Payment already sent | Phase 4: Business email compromise | Call the bank’s fraud team to request a recall | Finance lead |
| Attachment opened or file run | Phase 5: Contain malware | Isolate the device | Endpoint team |
Business email compromise is where speed matters most. The FBI’s Internet Crime Complaint Center recorded more than $3 billion in reported business email compromise losses in 2025, from almost 25,000 complaints, in its annual report published in April 2026. The IC3’s Recovery Asset Team works with banks through the Financial Fraud Kill Chain to freeze domestic transfers, and the FBI’s consistent advice is to contact your bank and file a complaint as quickly as possible. In the UK, Report Fraud replaced Action Fraud as the national reporting service for fraud and cyber crime in England, Wales and Northern Ireland from December 2025.
Session revocation is the step most often missed. Modern phishing kits capture the session cookie as well as the password, which lets an attacker bypass MFA without ever needing the code again. That is why Phase 3 revokes sessions and checks MFA methods, rules and app consents rather than stopping at a password reset, and why phishing-resistant authenticators such as passkeys and security keys appear among the improvement actions. NIST SP 800-63-4, finalised in 2025, requires verifiers at AAL2 to offer a phishing-resistant option.
Answer yes to “payment requested” and the fraud tasks appear assigned to the finance lead, not to the analyst who has never spoken to the bank. Answer no to everything and the checklist stays short. Nobody has to remember the right people to call at 4pm on a Friday.
Recipient lists, click lists and audit log exports are attached to the task that produced them. When a regulator or insurer later asks who clicked and what the attacker could read, the answer is in the record with a name and a time against it.
The closure phase asks for the lure and the warning signs, which gives the awareness programme real examples from your own inbox. Tags on each run make it easy to find every report from the same campaign or targeting the same team.
CheckFlow is not an email security gateway, SIEM or EDR tool, and it does not detect or remove phishing. It runs the human side of the response around those tools: who checks what, who calls the bank, and what was decided. For the wider set of security and compliance routines that sit around incident handling, CheckFlow’s compliance checklist software keeps owners, evidence and approvals in one place.
The cheapest phishing incident is the one that gets reported quickly. The Security Awareness Training Checklist runs the programme that teaches people to spot and report a lure, and the User Access Review Checklist removes the dormant and over-privileged accounts that make a stolen password more valuable. To rehearse the payment fraud branch with finance, use the Incident Response Tabletop Exercise Checklist.
Cybersecurity Incident Response Checklist
Security Awareness Training Checklist
User Access Review Checklist
Incident Response Tabletop Exercise Checklist
IT Incident Management Checklist
Describe the process in a sentence and the AI checklist generator drafts the phases and tasks for you.
Thank them, capture the original email with its headers, and ask what they did with it. Then search for every other copy, find out who else clicked or replied, purge it from all mailboxes and block the sender and links. If anyone entered a password, approved an MFA prompt, opened an attachment or acted on a payment request, follow the matching branch. Finally, tell the reporter what happened, which is what keeps people reporting.
Find out what happened after the click. If the page asked for a password and they entered it, treat the account as compromised: reset the password, revoke all sessions, and check MFA methods, inbox rules and app consents. If a file downloaded or ran, isolate the device. If they only opened the page and closed it, check the site and the proxy logs, record the outcome and close. Asking the user directly, without blame, is usually the fastest way to find out.
No. Many phishing kits steal the session cookie along with the password, so the attacker may stay signed in after a reset. Revoke all sessions and refresh tokens, remove any MFA method the user does not recognise, delete suspicious inbox rules and forwarding, revoke unfamiliar app consents, and review the audit logs to see what the attacker read or sent while they had access.
Call your bank’s fraud team straight away and ask them to recall the payment; the chance of recovery falls quickly as the money moves between accounts. In the US, file a complaint with the FBI’s IC3; in England, Wales and Northern Ireland, report to Report Fraud, which replaced Action Fraud. Then verify any other payment requests from that supplier on a known phone number, tell the supplier in case their mailbox is the one compromised, and notify your insurer if your policy covers social engineering fraud.
Generally not for a single click. Phishing is designed to fool careful people, and staff who expect blame report later or not at all, which turns a five-minute purge into an account takeover. Reward fast reporting, use real examples in training, and keep disciplinary routes for deliberate policy breaches. A repeat pattern is better handled with targeted coaching and stronger controls for that person’s role.
14-day free trial, no card required. The Business plan is $10 per user per month after the trial. Full details at checkflow.io/pricing.
14-day free trial, no credit cardFull refund in your first 30 daysUS hosting, EU on request