

An IT offboarding checklist is the ordered list of steps IT takes when someone leaves: block sign-in and revoke sessions, remove access in every app, revoke API keys and tokens, recover and wipe devices, hand over data, reclaim licences and keep a dated record of each step. For a dismissal, cut access before the person is told.
IT teams spend days onboarding a new hire — provisioning accounts, deploying devices, and setting up access to 30 or more systems. When that person leaves, the same access footprint needs to be dismantled completely, in a few hours, often under pressure. When it isn't, the cost is significant. A 2014 study by Intermedia and Osterman Research found that 89% of former employees still had access to at least one corporate application after leaving. Ponemon Institute's 2022 Cost of Insider Threats report puts the average cost of an insider threat incident at $15.38 million. This guide covers every phase of IT offboarding from a security perspective — what to do, in what order, and how to verify it's complete.
The IT Offboarding Checklist at a Glance
Before the last day
As soon as notice is accepted. For a dismissal, when HR books the meeting.
- HR confirms the last working day, the leaver type and an access cut-off time with IT
- IT lists the leaver's accounts, devices, admin roles and the shared passwords they can see
- The manager names the tools the team uses outside single sign-on and who takes over the work
- The leaver moves working files to shared locations and writes up what only they know
At the cut-off
The end of the last working day. During the meeting for a dismissal.
- IT blocks sign-in, revokes sessions and removes MFA methods
- IT disables VPN and remote access
- The manager or IT collects the laptop, phone, security keys and badge
Within 48 hours
- IT disables accounts in apps outside single sign-on
- IT revokes API keys, personal access tokens, SSH keys and OAuth grants, and rotates shared passwords
- IT moves files, the mailbox and admin roles to a named successor
Within two weeks
- IT wipes the devices and updates the asset register
- IT reclaims licences and removes group memberships
- IT runs a final access review and records the sign-off
Every phase below expands one of these lines.
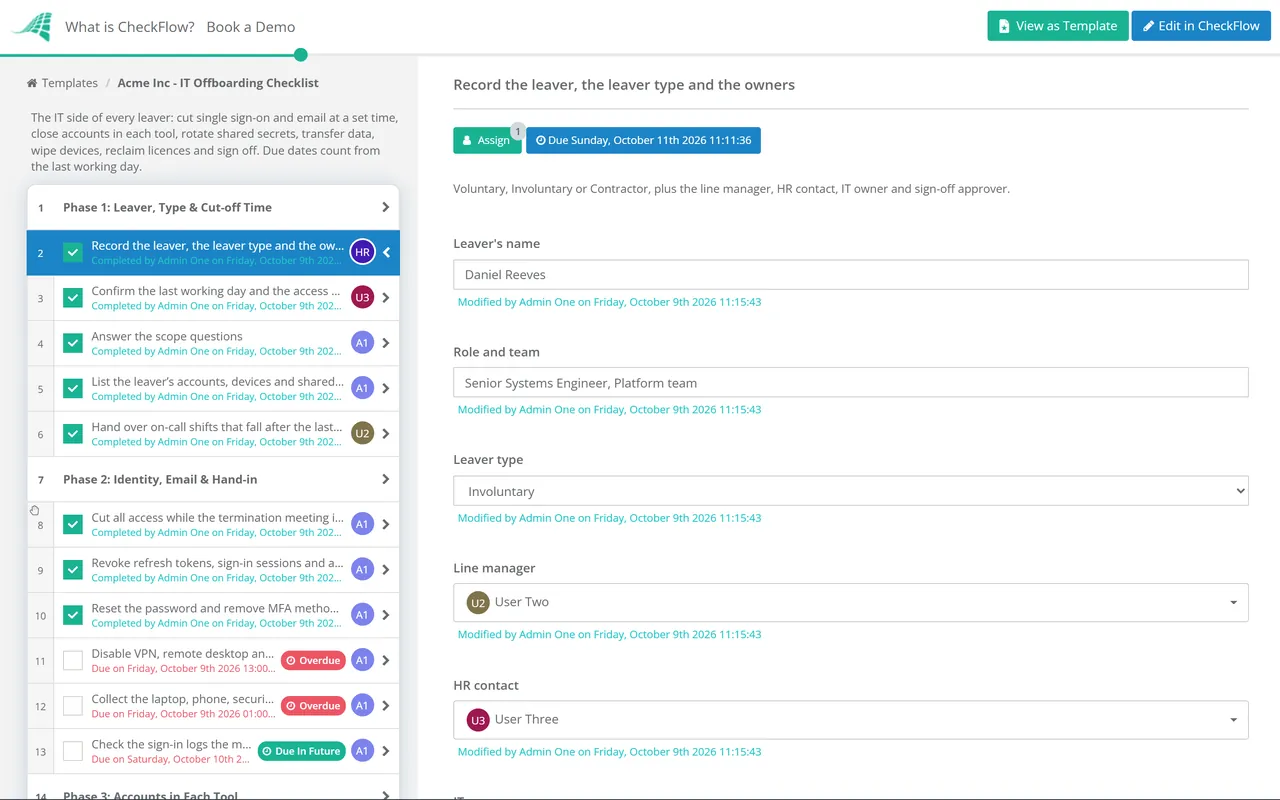
This is CheckFlow's free IT offboarding checklist template as a live checklist: seven phases, each step with an owner and a due date counted from the last working day. Try the live checklist.
Need it on paper? Add the template to a free trial, start a checklist for the leaver and print it, or save it as a PDF, from your browser's print dialog.
Why IT Offboarding Is a Security Problem
Offboarding is not an HR admin task — it is a security control point. The departing employee has legitimate credentials that security tools won't flag as anomalous. They know where the sensitive data is. They may be motivated. The numbers reflect the scale of the problem:
- 89% of ex-employees retained access to at least one app (Intermedia and Osterman Research, 2014)
- The average company ran 323 SaaS applications, and IT directly managed only 23% of them (Zylo SaaS Management Index, 2022)
- 71% of HR workers who offboarded someone in the past year had at least one leaver keep company equipment (Capterra, 2022)
The departing employee doesn't need to be malicious. A former colleague who can still log into Slack or read customer data in Salesforce represents an uncontrolled access risk — and an audit finding waiting to happen.
Compliance frameworks with specific offboarding controls:
- ISO 27001:2022 Annex A 5.11, 5.18 and 6.5: return of assets, removal of access rights, and the duties that still apply after someone leaves
- SOC 2 CC6.2 / CC6.3: remove logical access when it is no longer needed; auditors commonly expect it within 24 hours of termination
- NIST SP 800-171 (3.9.2): protect systems that hold CUI during and after terminations and transfers
Voluntary vs. Involuntary: The Timing Difference
This is one of the most practically important distinctions in IT offboarding and is frequently absent from generic checklists. The process is structurally different depending on departure type — and treating them the same way is a security failure.
Voluntary departure (resignation with notice period)
You have time to plan. Use the notice period for phased access reduction: begin removing admin rights and non-essential system access gradually while the employee is still working. Don't disable core working access until the last day.
A practical schedule: week one of notice — remove elevated and admin privileges; final week — restrict to read-only on sensitive systems; final day — full deprovisioning. The advantage is that knowledge transfer can happen, passwords for shared accounts can be captured, and documentation can be written. The employee is generally cooperative.
Watch for: data exfiltration during the notice period increases significantly. Monitor for large file downloads, emails to personal accounts, unusual after-hours access, and unexpected large data transfers. This is not about distrust — it is standard security posture for anyone with a confirmed departure date. Revoke full access at end of last working day, or when they hand in equipment, whichever comes first.
Involuntary termination (redundancy, dismissal, layoff)
The access revocation window is minutes, not days. The IT team must act before or simultaneously with the employee being informed. If the employee still has system access when they receive the news, the risk window is open.
The practical protocol: HR notifies IT 15–30 minutes before the termination meeting. IT blocks sign-in and revokes sessions the moment the meeting begins. The employee should not be able to log in by the time they return to their desk. Collect equipment immediately — do not allow a dismissed employee to return to their desk unsupervised after being informed.
Mass layoffs require coordination: if 50 people are being let go simultaneously, IT needs automated tooling to revoke access at scale, not a manual click-through for each account.
Common mistake: treating voluntary and involuntary departures identically. Treating a redundancy like a resignation — sending the departing employee a friendly email asking them to return equipment in the next two weeks — is a security failure. Involuntary departures require immediate action, not a courtesy timeline.
Who Does What: HR, IT and the Manager
| Role | Owns |
|---|---|
| HR | Tells IT the moment a departure is confirmed, sets the last day and the leaver type, books the exit meeting, records the exit interview |
| IT | Every access, account, key, device, data and licence step, and the audit record |
| Line manager | Names the tools and shared logins the team uses, decides who takes over files and accounts, signs off the handover |
Most gaps sit between these three. HR knows the date but not the systems; IT knows the systems but not the date; the manager knows which tools the team really uses. A checklist that gives each of them their own tasks, with due dates counted from the same last day, closes those gaps.
Phase 1: Immediate Actions (Within the First Hour)
These steps must happen in the first 60 minutes regardless of departure type.
Block sign-in at the identity provider
This is always first. In Microsoft Entra ID (formerly Azure AD): set "Block sign-in" to Yes. In Okta: deactivate the user (not just suspend — deactivation revokes all tokens). In Google Workspace: suspend the account. In on-premises Active Directory: disable the account in ADUC. This is the single most important action because it prevents any further authentication across all SSO-connected services.
Revoke all active sessions
Blocking sign-in does not kill existing authenticated sessions. Tokens already in use continue to work until they expire. In Entra ID: use "Revoke sessions" in the user's auth methods — this invalidates all refresh tokens immediately. In Okta: clear all active sessions from the user's profile. In Google Workspace: sign out all web sessions. In on-premises environments: flush Kerberos tickets. Without this step, an employee with an active laptop session can remain productive in cloud apps for hours after their account is blocked.
Change password immediately
Reset the account password to a randomly generated value that no one except the IT admin knows. This prevents any cached credential reuse. For SSO-only environments this matters less, but for environments with legacy apps accepting password auth directly, this is essential.
Remove MFA factors
Remove all registered MFA devices: authenticator app registrations, FIDO2 hardware keys, SMS numbers, backup codes. An attacker with stolen credentials can't get in if they don't have the MFA factor — but the legitimate ex-employee can still authenticate if their phone still has an active TOTP seed registered against the corporate account.
Notify relevant stakeholders
Alert: direct manager, HR, legal/compliance, security team, and any team leads whose systems the employee could access. For privileged users: notify the CISO. Trigger the ITSM ticket that tracks the full offboarding process — this is the record that will be reviewed during a compliance audit.
Phase 2: Identity & Access Revocation
With sign-in blocked and sessions revoked, the next phase is the systematic removal of access across all identity systems.
Directory services (AD / Entra ID / Okta / Google Workspace)
- Remove from all security groups and distribution lists — this removes access to shared mailboxes, SharePoint sites, Teams channels, and any group-based role assignments
- Remove all role assignments: check Azure AD roles, Okta group memberships, Google Workspace admin roles
- Remove from shared drives, shared mailboxes, and delegated access configurations
- Check for any guest account access (B2B invites) — these exist separately from the primary identity and are often missed
Microsoft 365 specific
- Convert the mailbox to a shared mailbox — preserves data without consuming a licence after the user licence is removed
- Remove all assigned licences including Copilot, Power Platform, and any add-ons
- Remove from all Teams channels, SharePoint sites, and OneDrive shared folders
- Review Power Automate flows owned by the user — flows break when their creator's account is disabled; reassign critical flows to a service account
- Review Copilot Studio agents if the employee created any — these can keep running after account deletion, accessing SharePoint data with no named owner (a 2026 blind spot most checklists miss)
- Submit a data subject request through Microsoft Purview if Copilot interaction history needs to be cleared (required under GDPR data minimisation)
Google Workspace specific
- Transfer ownership of all Google Drive content before the account is deleted — a deleted Google Workspace user can be restored for only 20 days
- Reset recovery email and phone to remove the employee's personal contact details
- Remove from Google Groups
VPN and remote access
- Revoke VPN certificates and remove VPN user from access lists — VPN clients often cache credentials locally, separate from directory
- Remove from any zero-trust network access (ZTNA) policies
- Delete remote desktop / RDP access permissions
Phase 3: SaaS Application Audit
This is where offboarding most commonly fails. Zylo's 2022 SaaS Management Index found the average company ran 323 SaaS applications, and IT directly managed only 23% of them. The rest — marketing tools, design platforms, project management apps, AI tools, developer utilities — are bought and run by business units, often with no IT visibility. Intermedia and Osterman Research found 89% of ex-employees retained access to at least one app.
Tier 1 — SSO-connected apps
When the IdP account is disabled, SSO-connected apps should refuse new logins. However: SCIM provisioning can take hours to propagate deactivation to downstream systems, and some apps cache sessions independently. Verify by checking each app's admin console directly, not just the IdP. High-priority SSO apps to verify explicitly: Salesforce, GitHub and GitLab, AWS / GCP / Azure, Slack and Microsoft Teams, Zendesk and Freshdesk, Jira and Linear, HubSpot and marketing platforms.
Tier 2 — Apps with local accounts bypassing SSO
These are the real risk. Even when SSO is enabled, many SaaS apps allow local login with an email and password as a fallback. The employee may have created an account before SSO was enforced, used a personal email address, or maintained a local password for convenience. Explicitly check and disable local accounts in: GitHub (check for personal accounts linked to org repos), AWS IAM console (IAM users are completely separate from SSO federation), Cloudflare and registrars, DNS providers, billing and payment platforms (Stripe, Paddle), and any tool where the employee held an admin role.
Tier 3 — Shadow IT (unknown apps)
Survey the manager and team about tools the employee used. Check expense reports for SaaS subscription charges. Review browser bookmarks if equipment is being returned. For high-risk departures, review SSO authentication logs for the past 90 days to see every app the user authenticated with — this gives you the most accurate access map of any approach available.
To run this phase for each leaver, with an app table, token revocation, data handover and licence reclaim in one record, use the free SaaS access offboarding checklist.
Automate Your IT Offboarding Process
CheckFlow lets IT teams run structured offboarding checklists with assigned tasks, due dates, and automatic audit trail records — so every departure is handled consistently, regardless of who's on shift. The free IT offboarding checklist template runs these phases in order, with a cut-off task only the IT owner can complete for involuntary exits.
Start free trial See IT TemplatesPhase 4: API Keys, Tokens & Privileged Credentials
This section often surprises non-technical managers: disabling an account does not revoke API tokens and keys. These are machine credentials that authenticate independently of the user's login session. If an employee created API keys, personal access tokens, or OAuth grants, those continue to work after the account is disabled unless explicitly revoked.
Personal access tokens (PATs)
GitHub, GitLab, Bitbucket, Jira, and most developer tools allow users to create PATs that authenticate API calls. These tokens never expire unless the creator sets an expiry date — and most don't. Revocation requires going into each platform's admin area and explicitly revoking each token. For GitHub, use the REST API to enumerate tokens owned by the user's account. For GitLab: Admin Area → Users → Access Tokens → revoke all. For Bitbucket: Admin → Users → App passwords → revoke.
SSH keys
SSH public keys registered in ~/.ssh/authorized_keys on servers, or in git hosting platforms, give direct shell access. They are completely unaffected by account disablement. Remove the employee's public key from authorized_keys on all servers they accessed. Check GitHub and GitLab admin user SSH key settings and remove. Review infrastructure automation tools — Ansible inventory files, Terraform state — for embedded keys.
AWS IAM access keys
AWS IAM users can have up to two long-lived access key pairs. These are completely independent of SSO federation and continue to work after the federated identity is disabled. Use aws iam list-access-keys --user-name [username] to find them, then aws iam delete-access-key to revoke. Also check IAM roles the user had permission to assume and any EC2 key pairs associated with the account.
OAuth grants and refresh tokens
When employees connect third-party apps to corporate systems, OAuth grants are created that persist beyond the user session. In Google Workspace: Admin Console → Security → API controls → App Access Control. In Microsoft 365: Entra ID → Enterprise Applications → review OAuth grants tied to the user.
Service accounts and shared credentials
If the employee created service accounts in their name, or knew passwords to shared accounts — database passwords, test environment credentials, shared admin accounts — rotate those immediately. Never assume the employee won't remember or reuse credentials they previously had access to.
Webhooks
Webhooks tied to a user's identity (Stripe, Segment, HubSpot) may use signing secrets that need to be rotated. If the employee managed integrations, audit and regenerate webhook secrets.
The 48-hour rule for non-human credentials: block interactive access immediately (Phases 1–2), but complete the full API key, token, and SSH key audit within 48 hours of departure. This is the window attackers exploit — the account is gone but the machine credentials remain active and undetected.
Phase 5: Device Recovery & Physical Access
Company-owned devices
Collect all hardware before the employee leaves the premises: laptop, mobile phone, tablet, hardware tokens (YubiKeys, RSA SecureID), USB drives, external drives, company-issued headsets and peripherals. Remote wipe via MDM (Microsoft Intune, Jamf, Workspace ONE) if equipment cannot be immediately retrieved — for remote employees, this is often the primary tool. For in-office employees: do not allow unsupervised return to desk after the termination meeting. Document serial numbers and asset tags at return, update the asset register, and wipe and reimage before reassignment.
Agree a return date with the leaver, check each item against the asset register when it comes back, and note any damage or missing kit in the offboarding record. A monthly IT asset management checklist then checks every leaver's returns against the register, so missing kit is chased while it can still be recovered.
BYOD (personal devices)
Personal devices hold corporate data but belong to the employee. Best practice: use MDM container or selective wipe to remove the corporate data container without touching personal data, revoke the device's MDM enrolment, and remove the corporate email profile. This should be covered in the employee's BYOD agreement signed at onboarding. In Capterra's 2022 survey, 71% of HR workers who offboarded someone in the past year had at least one leaver keep company equipment — a proactive asset register maintained throughout the employment lifecycle is the only reliable defence.
Physical access
- Deactivate access cards, key fobs, and building access codes immediately — this is often forgotten when the focus is on digital access
- Change any lock combinations or alarm codes the employee knew
- Retrieve any physical keys (server room, office, filing cabinets)
- Notify building security and reception to not admit the individual
Phase 6: Data Ownership Transfer
Departing employees often hold business-critical data in personal storage areas: Google Drive "My Drive", OneDrive, project repos, customer records. If not transferred before the account is deleted, this data can be lost permanently.
Email and calendar
- Convert mailbox to shared mailbox (Microsoft 365) or transfer to manager (Google Workspace) before removing licence — preserves access for continuity without consuming a licence
- Set up an out-of-office reply directing contact to the manager or designated successor
- Apply litigation hold if the employee's communications may be relevant to legal proceedings
- Google Workspace: use the data transfer tool to move Drive content and calendar ownership before account deletion
Files and documents
- Google Drive: use the admin data transfer tool to reassign all owned files to the manager
- OneDrive: grant manager access — Microsoft keeps a deleted user's OneDrive for 30 days by default (admins can change this), then 93 more days in a deleted state that only an admin can restore
- SharePoint sites where the employee was the only owner: assign a new owner before account deletion — ownerless SharePoint sites become inaccessible
- Shared Drives and SharePoint libraries are typically fine; personal drive content is the risk
Code and repos
- Transfer any GitHub or GitLab repos owned by the user to the organisation account (not another individual)
- Check for open PRs, active branches, and in-progress work — notify the team lead
- Check for CI/CD pipeline secrets stored in the user's personal space
Documentation and runbooks
- Ask the departing employee to document processes, credentials for shared accounts, and institutional knowledge during the notice period
- Confluence and Notion pages owned by the user: reassign or export
- Password manager entries: if the employee had entries for shared credentials (not personal), export and securely transfer those to the team vault
For regulated industries, data transfer must be logged. HIPAA requires documented evidence of who accessed what during the transfer process.
Phase 7: Email, Licensing & Post-Departure
Email continuation
- Set an auto-reply on the former employee's email for 30–90 days directing senders to the right contact
- Forward incoming emails to the manager or successor for business continuity
- Update any public-facing email addresses (website, LinkedIn company page, email signatures) that reference the departed employee
Licence reclamation
Every unused licence is wasted spend. Reclaim immediately after deprovisioning: Microsoft 365 and Google Workspace seats; Copilot, Power BI, and Power Apps add-on licences; Salesforce, HubSpot, and Zendesk seats; Adobe Creative Cloud; and any SaaS subscription associated with the user's email. Copilot licences alone run $30 or more per user per month — disciplined offboarding is often the fastest ROI in the process.
Post-departure audit (within two weeks)
- Run a SaaS discovery scan comparing the current access map against the offboarding checklist — any app that still shows the departed email address needs a manual revocation pass
- Verify all checklist items were completed; use the completed IT offboarding checklist as the audit evidence
- Confirm device has been wiped and asset register updated
- Update any documentation, runbooks, or system notes that named the departed employee as the owner or responsible party
Privileged & Admin Account Offboarding
Employees with admin-level access to cloud infrastructure, databases, or security tools require a separate protocol. The stakes are categorically higher.
What counts as privileged access: cloud infrastructure admin (AWS root or administrator, GCP Owner, Azure Owner); GitHub organisation owner or admin; Salesforce system admin; domain admin in Active Directory; Okta super admin; and any account with billing access, ability to create or delete users, or access to production data at scale.
Remove all admin roles first
Before completing standard access revocation, remove all admin roles. An admin account being disabled still represents a risk if role assignments persist and the account is re-enabled by mistake.
Rotate all shared admin credentials
Rotate any shared admin credentials the employee knew — never assume they didn't memorise the break-glass password or write it down. This includes emergency access accounts, root credentials, and any shared admin vault entries.
Review IAM policies and infrastructure-as-code
Review all IAM policies, service account permissions, and infrastructure-as-code (Terraform, CloudFormation) for resources created or last modified by the user. Resources created under their identity may carry their permissions implicitly.
Audit cloud logs for pre-departure activity
Audit CloudTrail, GCP Audit Logs, and Azure Activity Log for any unusual actions in the two weeks prior to departure. Look for: unusual data exports, new IAM key creation, permission escalation, or resource deletions.
Check scheduled jobs and automation scripts
Check for any scheduled jobs, cron tasks, or automation scripts that authenticate as the user or reference their personal credentials. These continue to run after the account is disabled and will either fail silently or — if credentials are embedded — continue to authenticate successfully.
Audit secrets management
For senior engineers who managed CI/CD: audit secrets management (HashiCorp Vault, AWS Secrets Manager) for any secrets scoped to the individual. Confirm that MFA enrolled on privileged accounts — hardware keys and so on — has been physically retrieved or remotely invalidated.
The most dangerous gap in privileged access offboarding is the "I'll do the audit later" approach. An ex-admin with a residual IAM key and knowledge of your AWS account structure doesn't need long. Do the privileged access audit immediately — not within 48 hours. Immediately.
Remote Employee Offboarding
Remote offboarding removes the ability to collect equipment in person, escort the employee from the premises, or verify the workspace. Everything must be done digitally — which requires specific adaptations.
- Device recovery: ship a prepaid return box as part of the offboarding workflow. Use MDM remote wipe (Intune, Jamf) as a backup if the device is not returned within the agreed window. Document the MDM wipe in the offboarding record.
- Access revocation: the same as in-office but with more emphasis on the API token and SSH key audit — remote employees are more likely to have personal development environments with embedded credentials.
- Physical access: you can't see the person remove their access badge or hand in their key. Triple-check physical access systems: did you deactivate their building access code even for a remote worker? If they ever visited the office, they may have an active access card.
- Knowledge transfer: more critical for remote employees who may have built processes, documentation, and tooling without colleagues seeing them work. Build document hand-off as a formal, assigned pre-departure task.
- Exit interview for IT: specifically ask remote employees about personal devices used for work, any accounts they created on personal email addresses, and any data stored locally that hasn't been synced to corporate systems.
Contractors, Shared Accounts and Role Changes
- Contractors and agency staff. Their end date sits in a contract IT may never see, so ask the engagement owner for it when the work starts. Remove guest accounts and sponsor links, recover company kit and get written confirmation that company data has been deleted from the contractor's own devices. For a supplier as a whole, use the vendor offboarding checklist.
- Shared accounts. A shared login has no single owner to disable. Rotate the password the day the leaver goes and move the account into a password vault with named users.
- Role changes. A move to another team is a partial offboarding: remove the access the old role needed before adding the new role's, or the person keeps both.
Common Mistakes That Create Security Incidents
Mistake 1: Disabling the account without revoking active sessions. The most common technical gap. Account disabled does not mean sessions terminated. An employee with an active browser tab in Gmail, Slack, or a cloud console remains active until the token expires — which can be hours. Always revoke sessions explicitly after disabling the account. In Microsoft Entra ID this is a separate action from blocking sign-in.
Mistake 2: Treating API keys as part of "account access". When IT disables an Okta account, that action does nothing to GitHub PATs, AWS IAM keys, or SSH keys created by that user. These are machine credentials with their own authentication path. They require explicit revocation from each system. Miss them, and the ex-employee can still push code to production repos, read S3 buckets, or access servers — without ever logging in through the corporate identity provider.
Mistake 3: Assuming SSO covers all SaaS access. SSO provides coverage for apps configured to use it — but in Zylo's 2022 index IT directly managed only 23% of the average company's SaaS apps. Many of the rest need manual revocation. Apps bought by marketing, design tools, AI assistants, and any tool where the employee signed up with a personal email address are invisible to the IdP. A post-departure SaaS audit is not optional.
Mistake 4: Skipping the notice period monitoring window. The period between resignation and departure is when data exfiltration is most likely. Employees back up files to personal storage, forward emails to personal accounts, and download contact lists. Monitoring departing employees within legal and policy boundaries during the notice period is standard security practice.
Mistake 5: No formal checklist — relying on tribal knowledge. When offboarding is handled ad hoc, the quality of the process depends entirely on who handles it that day. Senior engineers who leave know where the sensitive access lives; a junior IT person who doesn't know about the legacy AWS key doesn't know what they don't know. A structured, assigned, mandatory checklist removes the dependency on individual knowledge. The checklist doesn't forget. The person does. And because some departures will still slip through, a quarterly Active Directory and Entra ID account cleanup catches the accounts that were missed.
Compliance & Audit Trail Requirements
SOC 2 and ISO 27001 auditors use a consistent approach: they sample five ex-employees from the past 12 months and request evidence that access was revoked within the required timeframe. For each sampled employee they want:
- A timestamped access revocation log showing when the account was disabled
- Confirmation that licences were removed (proves no ongoing access to licensed tools)
- Device return or MDM wipe confirmation
- A completed offboarding checklist with named assignees and completion timestamps
If you can't produce these four items for each sampled employee, you have a finding. The finding is usually moderate for the first occurrence, significant if it's systemic.
SOC 2 (CC6.2 / CC6.3)
Access changes must be documented. CC6.2 and CC6.3 require access to be removed when it is no longer needed; the criteria set no hour count, but auditors commonly expect access to be revoked within 24 hours of departure.
ISO 27001 (Annex A 5.11, 5.18 and 6.5)
Annex A 5.11 covers the return of assets and 5.18 the removal of access rights; 6.5 covers the duties, such as confidentiality, that still apply after someone leaves. The policy must exist in writing and evidence of it being followed must be producible on request.
NIST SP 800-171 (3.9.2)
Used primarily by US defence contractors and federal suppliers. Requirement 3.9.2 asks you to protect systems that hold CUI during and after terminations and transfers: close accounts, recover property such as tokens and badges, and change access when someone moves role.
When each offboarding run is tracked as a CheckFlow IT offboarding checklist, the completion record automatically includes task name, who completed it, and timestamp. Print the completed checklist or save it as a PDF, or export checklist and task data, and auditors get a dated record of each step — no post-hoc reconstruction needed.
Retention requirements: keep offboarding records for a minimum of 3 years (SOC 2 audit cycles); 7 years for regulated industries (finance, healthcare). Store them in immutable storage (S3 Glacier or equivalent) where they cannot be modified after the fact.
Free IT Offboarding Templates
CheckFlow includes ready-to-use offboarding and IT process templates — free to try, fully customisable, and designed to run as live checklists with task assignments, due dates, and completion tracking. The templates below are built for IT and security teams and can be launched immediately from the CheckFlow IT template library.
Stop Rebuilding the Same Offboarding Checklist
CheckFlow lets IT teams run the employee offboarding template as a live, assigned checklist every time — with automatic task assignments, due dates, and a completion record that gives SOC 2 and ISO 27001 auditors a dated record of each step. No credit card required to start.
Start free trialHow CheckFlow Supports IT Offboarding
The root cause of most offboarding security failures is the same: no structured, enforced process that every team member follows every time, regardless of who's handling the offboarding. The senior engineer knows to check for IAM keys. The junior tech doesn't. A checklist removes that knowledge dependency entirely — the process carries the quality standard, not the individual running it.
CheckFlow is purpose-built for running the same process repeatedly with assigned tasks, due dates and automatic completion records. When an IT offboarding checklist is launched, every task is assigned to the right person, with a due date. A step can halt the checklist, so nothing after it can be ticked until it is done, and the cut-off task can be assigned to the IT owner alone; the completion record exists automatically. The Reports Grid shows every open offboarding across the organisation, live — no chasing for status updates. For teams using Zapier or API integrations, a new HR leaver ticket can auto-launch the offboarding checklist with employee name, department, departure date, and manager pre-filled from the HR system. The IT team doesn't even need to start it — the process starts itself.
For MSPs managing offboarding for multiple clients, CheckFlow handles concurrent offboardings — ten clients' departing employees can all have live offboarding checklists running simultaneously, each with their own assignees and timelines, all visible in the Reports Grid. This is the use case that spreadsheets and PSA tickets fundamentally can't match at scale. When a whole client ends its contract with you, the checklist for when a client leaves your MSP covers handing back admin rights, domains and licences and removing your own tools.
Conclusion
IT offboarding is a security control, not a farewell ceremony. The seven-phase structure covered in this guide — immediate access block, identity revocation, SaaS audit, API and token cleanup, device recovery, data transfer, and post-departure tasks — is what complete offboarding looks like in practice. A structured, assigned checklist is the only reliable way to ensure all 40-plus steps happen every time, regardless of who's handling it.
The organisations that pass SOC 2, ISO 27001, and NIST audits without drama aren't working harder — they're running the same rigorous process every time an employee leaves, and the audit evidence is already there when the auditor asks for it. A verifiable, timestamped offboarding record isn't an administrative overhead; it's the proof that your security controls are operational, not just documented.
Frequently Asked Questions
What is the most important first step in IT offboarding?
Block sign-in and revoke all active sessions in your identity provider (Active Directory, Entra ID, Okta, or Google Workspace) before anything else. This prevents token-based access continuing even after a password change. For involuntary terminations, this must happen simultaneously with or before the employee is notified.
How long after an employee leaves should access be revoked?
SOC 2 CC6.2/CC6.3 require access to be removed when it is no longer needed, and auditors commonly expect it documented and revoked within 24 hours. NIST SP 800-171 3.9.2 requires systems to be protected during and after terminations. ISO 27001 Annex A 5.11 and 5.18 cover the return of assets and the removal of access rights. Best practice for privileged accounts is immediate revocation; for standard accounts, revoke by end of last working day at the latest.
What does IT offboarding miss most often?
SaaS apps outside SSO, OAuth tokens and API keys (which persist after account disable), SSH keys in authorized_keys files, and service accounts created in the employee's name. A 2014 Intermedia and Osterman Research study found 89% of ex-employees retained access to at least one app after leaving.
What is the difference between voluntary and involuntary IT offboarding?
For voluntary departures, access is typically revoked at end of last business day, with a notice period allowing knowledge transfer. For involuntary terminations, access must be disabled immediately — ideally before or during the termination conversation — to prevent data exfiltration.
What audit evidence does IT need to produce for offboarding compliance?
Auditors (SOC 2, ISO 27001) typically sample five ex-employees and request: timestamped access revocation logs, confirmation of licence removal, evidence of device return or remote wipe, and a completed offboarding checklist with named assignee and completion timestamp. A structured checklist tool like CheckFlow produces this evidence automatically.
Related Articles
Run Every IT Offboarding Consistently — With a Full Audit Trail
CheckFlow's IT offboarding checklist software gives every departure a structured, assigned, timestamped process. Free trial, no credit card required.
Start free trial Book a Demo